Michalis Botas on SKAI 100.3: Digital Dependency, Critical Infrastructure and the Need for Resilience
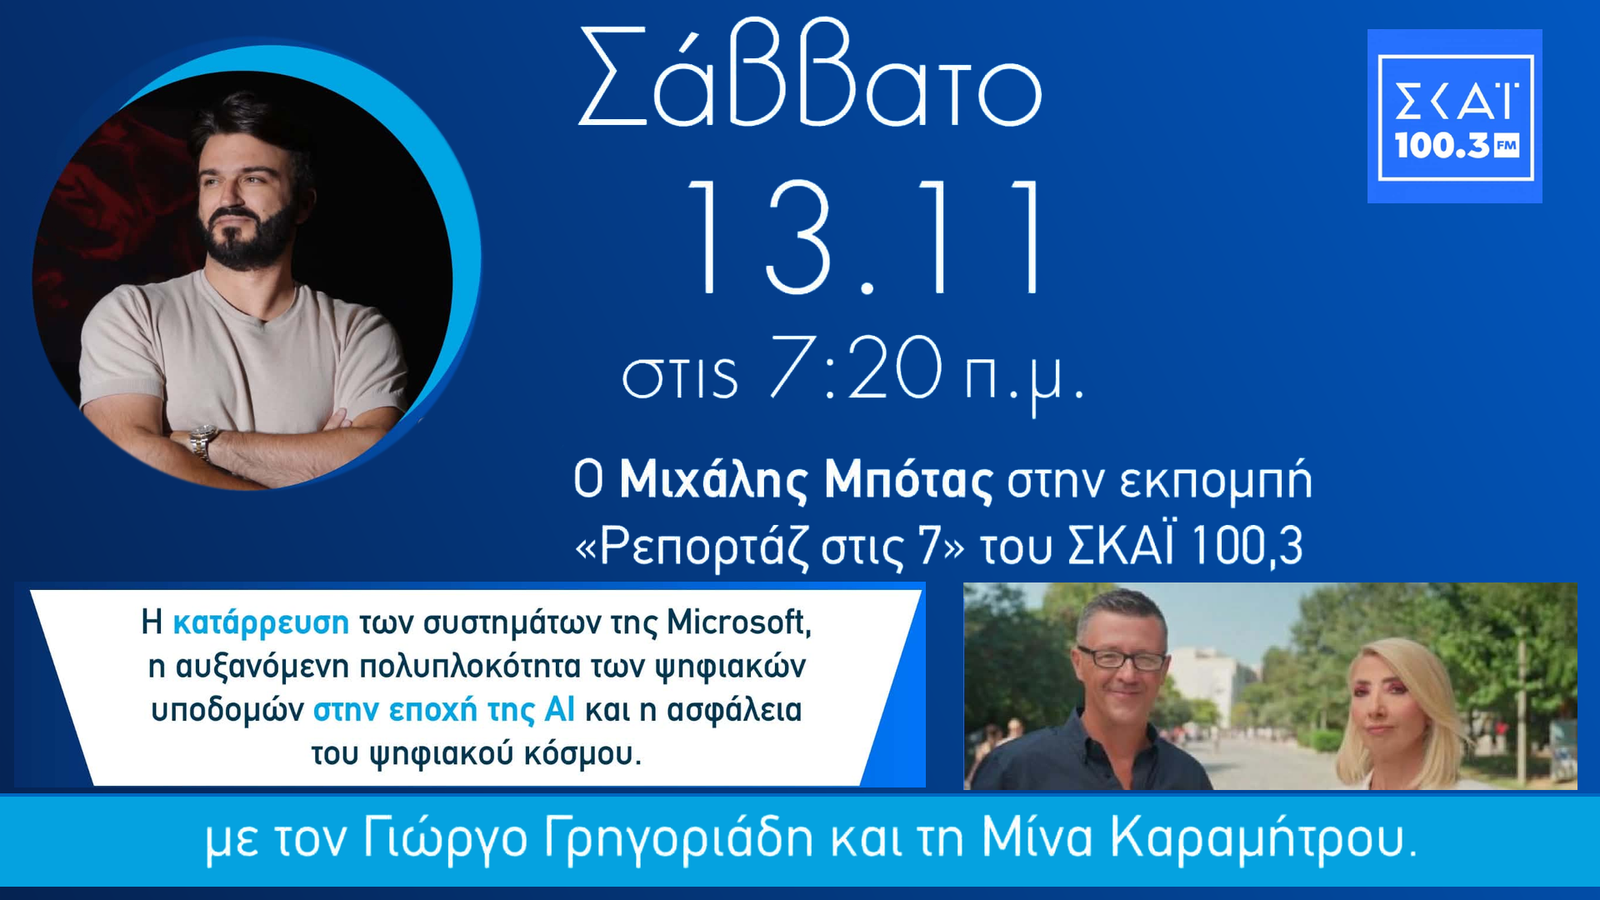
The growing dependence of modern societies on interconnected digital systems and the risks facing critical infrastructure were central themes of an interview with Michalis Botas, founder of DMSS Marketing Agency and a Digital Marketing instructor, on Greece’s SKAI 100.3 radio station on Saturday, November 14, 2026. Speaking to journalists Mina Karamitrou and Giorgos Grigoriadis on the news program “Reportaz stis 7,” Michalis Botas discussed how technological disruptions can affect transportation, banking, healthcare, supply chains, and other essential services. His central message was that increasingly interconnected digital infrastructure requires reliable contingency planning and alternative systems.
The discussion followed a major disruption affecting Microsoft services and widespread problems in United States air transportation, two separate incidents that brought digital infrastructure resilience into the international spotlight.
Although the events involved different systems and circumstances, both demonstrated the potential consequences of technological failures for organizations and the public.
The interview also raised a broader question: as businesses, governments, and individuals become increasingly dependent on digital platforms, who is responsible for ensuring that essential services remain available when those platforms fail?
For international audiences, the discussion offers an opportunity to examine digital resilience beyond the immediate context of the incidents. It connects technological dependency with public-private cooperation, infrastructure governance, business continuity, and regulatory developments in Europe and the United States.
The original interview is available through the official SKAI 100.3 broadcast archive for November 14, 2026.
The interview excerpts quoted below are English translations of statements made during the original Greek-language broadcast.
Michalis Botas on SKAI 100.3: Why Everything Is Connected
The interview began with concerns about technological disruptions and their potential consequences for ordinary users.
Journalist Mina Karamitrou raised a familiar question: could the recent technical problems expose personal information, including the contents of email accounts?
Botas responded by directing attention toward the wider consequences of technological interdependence.
Michalis Botas: “The point is that everything is connected.”
He explained that when one essential system stops working, the consequences can extend beyond that system and affect other activities.
“Something stops working, and suddenly other things stop working too,” he observed.
This distinction is important because digital infrastructure is rarely limited to an isolated application.
A company may use one platform to communicate with clients, another to coordinate its employees, and a third to manage inventory. Yet these apparently separate services may rely on common cloud infrastructure, authentication systems, networking components, or software providers.
A failure affecting one shared dependency can therefore disrupt several activities at once.
For the wider economy, such problems can become particularly serious when they affect organizations providing essential services.
The central concern is not simply whether a popular application is temporarily unavailable. It is whether the failure of that application or an underlying system can prevent other organizations from delivering services on which people depend.
Digital Dependency as a Global Infrastructure Challenge
Digital transformation has made businesses and public services faster, more interconnected, and increasingly accessible.
Cloud computing, integrated communications platforms, automated systems, and digital payments have created opportunities for organizations to operate efficiently across national borders.
However, these developments have also introduced new dependencies.
A company headquartered in one country may rely on cloud services operated internationally, software maintained by a different provider, and telecommunications networks connecting multiple regions.
When a critical component becomes unavailable, the resulting disruption may extend well beyond the geographical location where the technical problem originated.
Why Shared Technology Creates Interconnected Risks
Shared digital services offer significant economic and operational advantages.
Organizations can access advanced technology without maintaining every server, network, or application internally.
For smaller businesses, this can reduce technical complexity and provide access to capabilities that would otherwise require substantial investment.
For larger organizations, common platforms can simplify international coordination.
Nevertheless, these benefits come with the responsibility to understand the dependencies they create.
A failure affecting a shared identity service, for example, could prevent users from accessing several applications even if those applications remain operational.
Similarly, a problem involving a central communications platform may affect customer support, internal coordination, and time-sensitive transactions.
The consequences depend on the specific architecture, the duration of the disruption, and the availability of alternative procedures.
Critical Infrastructure Extends Beyond the Technology Sector
Critical infrastructure includes systems and services whose interruption can seriously affect public welfare, safety, and economic activity.
These include transportation networks, healthcare facilities, energy systems, financial services, water supplies, and digital communications.
The European Commission’s framework for critical infrastructure resilience recognizes the importance of protecting essential services across multiple sectors.
The challenge is particularly complex because failures do not necessarily remain confined to one sector.
A disruption affecting communications or logistics systems may create problems for organizations that depend on those services to deliver goods, coordinate personnel, or exchange essential information.
This interconnected structure formed the foundation of Botas’s remarks during the SKAI interview.
The November 2026 Microsoft Outage and Its International Impact
The global disruption affecting Microsoft services in November 2026 provided an example of the operational consequences of digital dependency.
Outlook, Teams, Copilot, and related services experienced widespread availability problems, affecting business communications and other organizational activities.
According to Reuters reporting published on November 14, 2026, Microsoft announced that its services had recovered following an outage lasting more than 24 hours.
The disruption affected organizations in several countries, preventing users from accessing functions such as email, calendars, and online meetings.
Some financial and corporate organizations were forced to adopt alternative communications procedures while the affected services remained unavailable.
Microsoft attributed the incident to technical server problems and reported that it had found no evidence of malicious activity.
The outage therefore illustrates an important distinction: a major technological disruption does not necessarily involve a cyberattack or a personal data breach.
Why Availability Can Matter as Much as Data Security
Cybersecurity discussions often focus on unauthorized access, stolen information, and malicious attacks.
These threats are important, but they represent only part of the broader challenge of digital reliability.
The availability of systems is equally relevant to organizations whose operations depend on continuous access to digital services.
A hospital may require access to administrative and clinical information systems. A logistics provider may need operational data to coordinate deliveries. A financial institution may depend on secure communications to complete time-sensitive procedures.
In such circumstances, a temporary loss of availability can create operational problems even when confidential information has not been compromised.
For this reason, digital resilience must address both malicious threats and ordinary technical failures.
The United States Aviation Disruption: A Different Incident, Similar Questions
During the radio interview, Giorgos Grigoriadis also discussed serious problems affecting air transportation in the United States.
The conversation reflected uncertainty surrounding the causes of the disruption, including speculation about outdated systems and the possibility of unauthorized interference.
Botas expressed concern about the difficulty of determining the causes of major technological incidents while they are still unfolding.
Subsequent official statements clarified the circumstances of the aviation disruption.
According to the Federal Aviation Administration’s official questions and answers, published on November 15, 2026, a technical problem on November 13 resulted in a nationwide ground stop.
The FAA explained that legacy telecommunications equipment became unstable following unusually heavy network traffic. The resulting problems affected communications and radar feeds used by air traffic control facilities.
The nationwide ground stop was implemented as a precautionary safety measure, and flights subsequently resumed.
Importantly, the FAA stated that available evidence did not indicate a cyberattack or malicious outside involvement.
There is also no established evidence that the FAA incident and the Microsoft outage were caused by the same technical problem.
What Aviation Systems Reveal About Infrastructure Resilience
Air transportation demonstrates why digital resilience must include operational safeguards.
Technology supports flight coordination, communications, scheduling, and numerous services required for modern aviation.
However, aviation safety also relies on trained personnel, established procedures, alternative capabilities, and decisions designed to manage uncertainty.
The FAA’s response illustrates the importance of maintaining safety procedures when a technological system becomes unstable.
The broader lesson is not that interconnected digital systems should be abandoned.
Instead, organizations responsible for essential services must be prepared to manage failures without allowing a technical problem to automatically become an uncontrolled safety crisis.
This principle is relevant across many other sectors, including healthcare, energy, telecommunications, and financial infrastructure.
From Cybersecurity to Operational Resilience: The European Approach
Europe has increasingly recognized that protecting digital systems requires more than preventing unauthorized access.
The ability to maintain essential functions, respond to disruptions, and restore services has become an important component of European policy.
Several legal and strategic frameworks address different aspects of this challenge.
NIS2: Strengthening Cybersecurity Across Critical Sectors
The European Union’s NIS2 Directive establishes a common cybersecurity framework covering 18 critical sectors.
Its scope includes areas such as energy, transportation, healthcare, banking, digital infrastructure, and public administration.
The directive introduces requirements concerning cybersecurity risk management, incident reporting, organizational responsibility, and cooperation between competent authorities.
It also emphasizes supply chain security and the role of organizational leadership in managing cybersecurity risks.
NIS2 does not mean that every business is subject to identical obligations.
Its requirements apply to entities that fall within the relevant scope, taking into account sector-specific and organizational criteria.
Nevertheless, it reflects a broader policy development: cybersecurity and continuity planning are increasingly regarded as responsibilities that extend beyond an organization’s technical department.
The Critical Entities Resilience Directive
The European Union also addresses the continuity of essential services through the Critical Entities Resilience Directive.
This framework focuses on strengthening resilience across 11 essential sectors, including healthcare, transport, energy, banking, food supply, water services, and digital infrastructure.
Its approach considers a wider range of potential disruptions, including natural hazards, accidents, and deliberate acts.
This broader perspective is significant because not every infrastructure failure is caused by a cyberattack.
Resilience planning must also account for physical damage, equipment failures, human error, and other events capable of interrupting essential services.
DORA: Digital Resilience in the Financial Sector
The financial sector faces specific risks because the reliable operation of digital systems is central to banking, payments, investment services, and financial market infrastructure.
The European Union’s Digital Operational Resilience Act, known as DORA, has applied since January 17, 2025.
According to the European Securities and Markets Authority (ESMA), DORA establishes requirements intended to strengthen the ability of financial entities to withstand, respond to, and recover from information and communication technology disruptions.
It also addresses risks associated with external technology providers.
DORA is not a general requirement applying to every organization. Its scope is focused on financial entities and relevant technology-service arrangements.
Together, NIS2, the Critical Entities Resilience Directive, and DORA illustrate how different European frameworks contribute to the wider objective of maintaining reliable essential services.
Technology Providers, Supply Chains and the Risk of Concentration
One of the most significant themes emerging from Botas’s interview is the concentration of digital activity around major technology providers.
Large platforms offer valuable services, but organizations may become dependent on common underlying technologies.
These dependencies can involve cloud infrastructure, authentication, storage, communications tools, or specialized software.
The resulting risk is not determined simply by the size of the provider.
It depends on how the organization’s systems are designed and whether critical services can continue when a particular component is unavailable.
The EU ICT Supply Chain Security Toolbox
On February 13, 2026, the European Commission announced the EU ICT Supply Chain Security Toolbox.
The initiative provides a common approach for identifying, assessing, and mitigating cybersecurity risks across technology supply chains.
Its recommendations include evaluating critical suppliers, considering multi-vendor strategies, and addressing dependencies on high-risk providers.
The toolbox represents a non-binding approach to risk management rather than a universal requirement for all organizations to adopt multiple providers.
It nevertheless highlights an increasingly important question for businesses and public institutions: how much of their operational continuity depends on technologies controlled by external suppliers?
Does Using Multiple Providers Automatically Improve Resilience?
Not necessarily.
Using more than one technology provider may reduce some concentrated dependencies, but it can also introduce additional complexity.
Two supposedly independent services may still rely on the same network, authentication provider, or supporting infrastructure.
A truly resilient arrangement requires an understanding of these relationships.
For some organizations, a carefully tested alternative communications system may provide meaningful protection.
Others may require more advanced arrangements involving independent infrastructure, additional suppliers, or separate recovery environments.
The appropriate strategy depends on the importance of each function, the available resources, and the consequences of a potential interruption.
The United States Perspective: Managing Risk Through the NIST Framework
While European policy includes sector-specific legal obligations, the United States also provides widely used frameworks for managing digital risk.
The National Institute of Standards and Technology Cybersecurity Framework 2.0 offers guidance for organizations seeking to improve their cybersecurity risk management.
The framework is organized around six functions:
- Govern: Establish responsibilities and risk management policies.
- Identify: Understand important systems, assets, and dependencies.
- Protect: Implement safeguards to reduce exposure to risks.
- Detect: Recognize potentially harmful incidents and anomalies.
- Respond: Manage incidents and limit their consequences.
- Recover: Restore affected systems and operations.
The framework is designed to be adaptable to different organizational circumstances.
Its value extends beyond specific technical tools.
It encourages organizations to connect cybersecurity decisions with leadership, operational priorities, and the management of business risks.
For internationally active organizations, these principles can complement applicable laws and sector-specific requirements.
A multinational company, for example, may need to comply with European regulatory obligations while using NIST guidance to organize its broader risk management processes.
Michalis Botas: Why Backup Government Infrastructure Matters
The central message of the SKAI interview emerged when the discussion turned toward society’s increasing reliance on technology.
Mina Karamitrou questioned whether everyday life had become excessively dependent on electronic systems.
Giorgos Grigoriadis agreed that technological dependency had become an unavoidable feature of modern society.
Botas acknowledged the difficulty of reducing reliance on major technology companies and stressed the importance of backup infrastructure.
Michalis Botas: “There definitely need to be backup government systems.”
The statement reflected his argument that governments should maintain alternative arrangements capable of supporting essential functions when major digital services become unavailable.
His position was not a call to abandon technology.
Rather, it emphasized the need to prepare for disruptions that may affect a substantial part of the economy and society.
Public-Private Cooperation and Essential Services
Public institutions frequently depend on privately developed or operated technologies.
Cloud platforms, telecommunications networks, software applications, and infrastructure support services can involve multiple public and private organizations.
This creates a shared responsibility for managing risks.
Governments establish legal requirements, oversee essential services, and coordinate public emergency responses.
Private providers are responsible for operating their systems, maintaining appropriate safeguards, and meeting relevant contractual and legal obligations.
Organizations using these services also need to understand their own dependencies and develop appropriate contingency plans.
Effective resilience requires cooperation between these groups.
A government cannot necessarily replace every commercial technology service, just as a private technology company cannot independently assume responsibility for the continuity of all public services.
The practical objective is to establish clear roles, appropriate alternatives, and coordinated procedures before a major disruption occurs.
Business Continuity Beyond Backups: What Organizations Should Prepare For
Backup infrastructure is an important part of resilience, but operational continuity requires a broader approach.
An organization may have copies of its data and still be unable to deliver services if its communications, authentication, or logistical systems become unavailable.
Preparing for such situations involves understanding which activities are essential and determining how they can continue during an interruption.
Mapping Critical Dependencies
Organizations should identify the systems, suppliers, and services supporting their most important operations.
This assessment should extend beyond the applications employees use directly.
It may also include infrastructure providers, network services, identity management systems, and third-party integrations.
Without understanding these dependencies, it can be difficult to determine whether an alternative solution is genuinely independent.
Establishing Alternative Communications
Major service interruptions may prevent teams from using their normal email or collaboration platforms.
Organizations can reduce this risk by establishing secure alternative communications procedures.
Such arrangements should be planned and tested in advance.
Adopting an unfamiliar messaging platform during a crisis without assessing security and privacy requirements may introduce additional problems.
Testing Recovery and Continuity Procedures
Business continuity plans should be evaluated through realistic exercises.
An organization might simulate the unavailability of email, a cloud platform, or an essential internal application.
The objective is to identify gaps before a real incident occurs.
Exercises can also help staff understand their responsibilities and improve coordination between technical teams, management, and external providers.
Prioritizing Essential Services
Not every function needs to be restored at the same time.
Organizations should determine which services are most important to safety, customers, and ongoing operations.
This prioritization can help guide recovery decisions when technical resources are limited.
For critical infrastructure operators, continuity planning may also need to account for physical safety requirements and legal obligations.
Artificial Intelligence and the Next Generation of Digital Dependencies
Artificial intelligence adds another dimension to the discussion of digital resilience.
Organizations increasingly use AI-supported systems for data analysis, customer interactions, workflow automation, and operational decision support.
Many of these applications depend on external platforms, cloud computing resources, and interfaces connecting different services.
As a result, AI adoption can create additional dependencies that need to be considered in operational planning.
However, it is important to distinguish this general trend from the causes of specific technical incidents.
The available official information concerning the November 2026 Microsoft and FAA disruptions did not establish that artificial intelligence caused either incident.
The broader question is how organizations can introduce AI systems responsibly while preserving suitable human oversight and alternative procedures.
Why Human Oversight Still Matters
An organization using an external AI service for customer support or internal information processing should consider what happens when that service is temporarily unavailable.
Can employees continue the essential process manually?
Are appropriate records available without relying exclusively on the AI system?
Is responsibility for important decisions clearly assigned to qualified personnel?
These questions are particularly relevant when automated systems support functions that cannot be interrupted without serious consequences.
The responsible adoption of AI therefore involves more than selecting effective tools. It also requires evaluating reliability, data protection, operational dependencies, and the need for human intervention.
Botas has discussed the broader transformation caused by artificial intelligence in previous media appearances and interviews.
In an earlier Market Insiders podcast interview, presented in the article “Michalis Botas: How AI Brings Tomorrow into Today’s Marketing”, he examined AI’s implications for productivity, digital marketing, and employment.
His subsequent SKAI interview approached digital transformation from another perspective: the risks associated with depending on increasingly interconnected technological systems.
Why Europe Encourages 72-Hour Emergency Preparedness
Another issue mentioned during the SKAI discussion was the preparation of citizens for disruptions affecting essential services.
Botas referred to European discussions about maintaining basic supplies during emergencies, connecting the subject with society’s reliance on functioning infrastructure.
The European Commission’s Preparedness Union Strategy, presented in March 2025, addresses a broad range of potential crises.
One of its initiatives involves developing guidance intended to help the population remain self-sufficient for at least 72 hours.
The strategy covers multiple risks, including natural disasters, public health emergencies, geopolitical disruptions, and interruptions affecting essential services.
It is not a warning that a particular technological collapse is imminent.
Instead, the initiative reflects the broader principle that societies benefit from planning for unexpected disruptions.
For citizens, emergency preparedness may involve maintaining essential supplies and knowing how to obtain reliable information.
For organizations and public authorities, the same principle takes a more complex form through continuity planning, emergency coordination, and resilient infrastructure.
The International Lesson: Resilience Must Evolve Alongside Digital Innovation
The discussion on SKAI 100.3 highlights a challenge that is relevant far beyond Greece.
Modern societies depend on technology for communication, economic activity, transportation, healthcare, and access to public services.
That dependence offers substantial advantages, but it also makes the reliability of shared digital infrastructure increasingly important.
The Microsoft outage demonstrated how a technical problem can affect organizations internationally.
The FAA incident showed how instability in critical telecommunications infrastructure can require major operational measures even without evidence of a cyberattack.
European regulatory initiatives and the NIST Cybersecurity Framework reflect different approaches to improving risk management and operational continuity.
Together, these developments point toward an important conclusion.
Digital progress should not be measured only by the number of services that can be automated or connected. It should also be evaluated by the ability of those services to remain reliable, recover from disruptions, and support essential activities under difficult conditions.
The concerns raised by Michalis Botas during his radio interview therefore extend beyond the immediate events of November 2026.
They touch on an increasingly important question for governments, businesses, and citizens worldwide: how can societies benefit from advanced technology without becoming unprepared for the consequences of its occasional failure?
Listen to Michalis Botas on SKAI 100.3
Michalis Botas appeared on SKAI 100.3 on Saturday, November 14, 2026, during the program “Reportaz stis 7”, hosted by journalists Mina Karamitrou and Giorgos Grigoriadis.
The full radio broadcast can be accessed through the official SKAI 100.3 episode archive.
Listen to an excerpt from Michalis Botas’s interview in the video below.
The interview examines the consequences of digital dependency and the importance of backup infrastructure in an increasingly interconnected world.
Further Reading: Michalis Botas and Digital Dependency
For readers interested in exploring the issues raised during the SKAI interview, four complementary Greek-language articles examine the subject from different editorial perspectives.
OpinionFeed.gr (Greek-language article): The published feature “Michalis Botas on SKAI 100.3: Digital Dependency, Critical Infrastructure and the Need for a Backup Plan” focuses on public responsibility, the protection of essential services, and the importance of alternative government infrastructure.
Market Insiders (Greek-language article): “Michalis Botas on SKAI 100.3: The Cost of Digital Outages to the Real Economy” examines the financial consequences of technology disruptions, lost productivity, business continuity, and operational risks.
Targeted.gr (Greek-language article): “Michalis Botas on SKAI 100.3: Dependence on Technology Giants and the Digital Future” explores major digital platforms, cloud infrastructure, technological concentration, and strategies for reducing dependence on individual providers.
PrimeLife.gr (Greek-language article): “Michalis Botas on SKAI 100.3: How a Technology Outage Affects Everyday Life” examines the practical impact of digital disruptions on personal communications, payments, transportation, and access to essential services.
These English titles are translations provided for international readers. The original publications are written in Greek and explore complementary aspects of the same radio interview.
Frequently Asked Questions (FAQ)
Who is Michalis Botas?
Michalis Botas is a Greek Digital Marketing Specialist, Digital and Social Media Marketing instructor, and founder of DMSS Marketing Agency and the NexMedia Publishing Network.
He has more than 15 years of professional experience in digital marketing and online communication. His work includes SEO, Digital PR, brand development, AI SEO, Generative Engine Optimization (GEO), Answer Engine Optimization (AEO), and AI Visibility.
He has also participated in media interviews and radio discussions addressing technology, digital communication, and the influence of artificial intelligence on businesses.
When did Michalis Botas appear on SKAI 100.3?
Michalis Botas appeared on Saturday, November 14, 2026, during the radio program “Reportaz stis 7,” hosted by Mina Karamitrou and Giorgos Grigoriadis.
What was the main subject of the interview?
The discussion focused on technological dependency, the consequences of disruptions affecting interconnected digital services, and the need for backup infrastructure and contingency planning.
Why are modern societies dependent on major technology providers?
Businesses and public institutions use digital platforms for communication, computing, data storage, and operational coordination. When multiple services depend on common infrastructure, a disruption affecting that infrastructure can influence several activities simultaneously.
Was the November 2026 Microsoft outage caused by a cyberattack?
According to Microsoft’s public statements following the incident, the disruption was attributed to technical problems, and the company had found no evidence of malicious activity.
Was the United States aviation disruption connected to the Microsoft outage?
No causal connection between the incidents has been established. The FAA attributed its November 13, 2026 disruption to technical instability affecting telecommunications systems and reported no indication of a cyberattack.
What is digital operational resilience?
Digital operational resilience refers to an organization’s ability to maintain, adapt, or restore important operations when its information and communication technology systems experience serious disruptions.
What are NIS2 and DORA?
NIS2 is a European Union directive establishing cybersecurity requirements across critical sectors. DORA is an EU regulation addressing digital operational resilience in the financial sector. They have different scopes and requirements.
Why are backup systems important for critical infrastructure?
Backup systems and alternative procedures can help organizations maintain essential functions during technological disruptions. Their effectiveness depends on appropriate design, independence from affected components, and regular testing.
Why does the European Union discuss 72-hour emergency preparedness?
The European Commission’s Preparedness Union Strategy includes an initiative to develop guidance for maintaining access to basic necessities for at least 72 hours during emergencies. It addresses multiple types of crises and is not limited to cyber incidents.
Where can I listen to the Michalis Botas interview?
The full broadcast is available through the official SKAI 100.3 episode page. A video excerpt is also available on YouTube.